Observing Android’s Binder Trust Boundary with eBPF
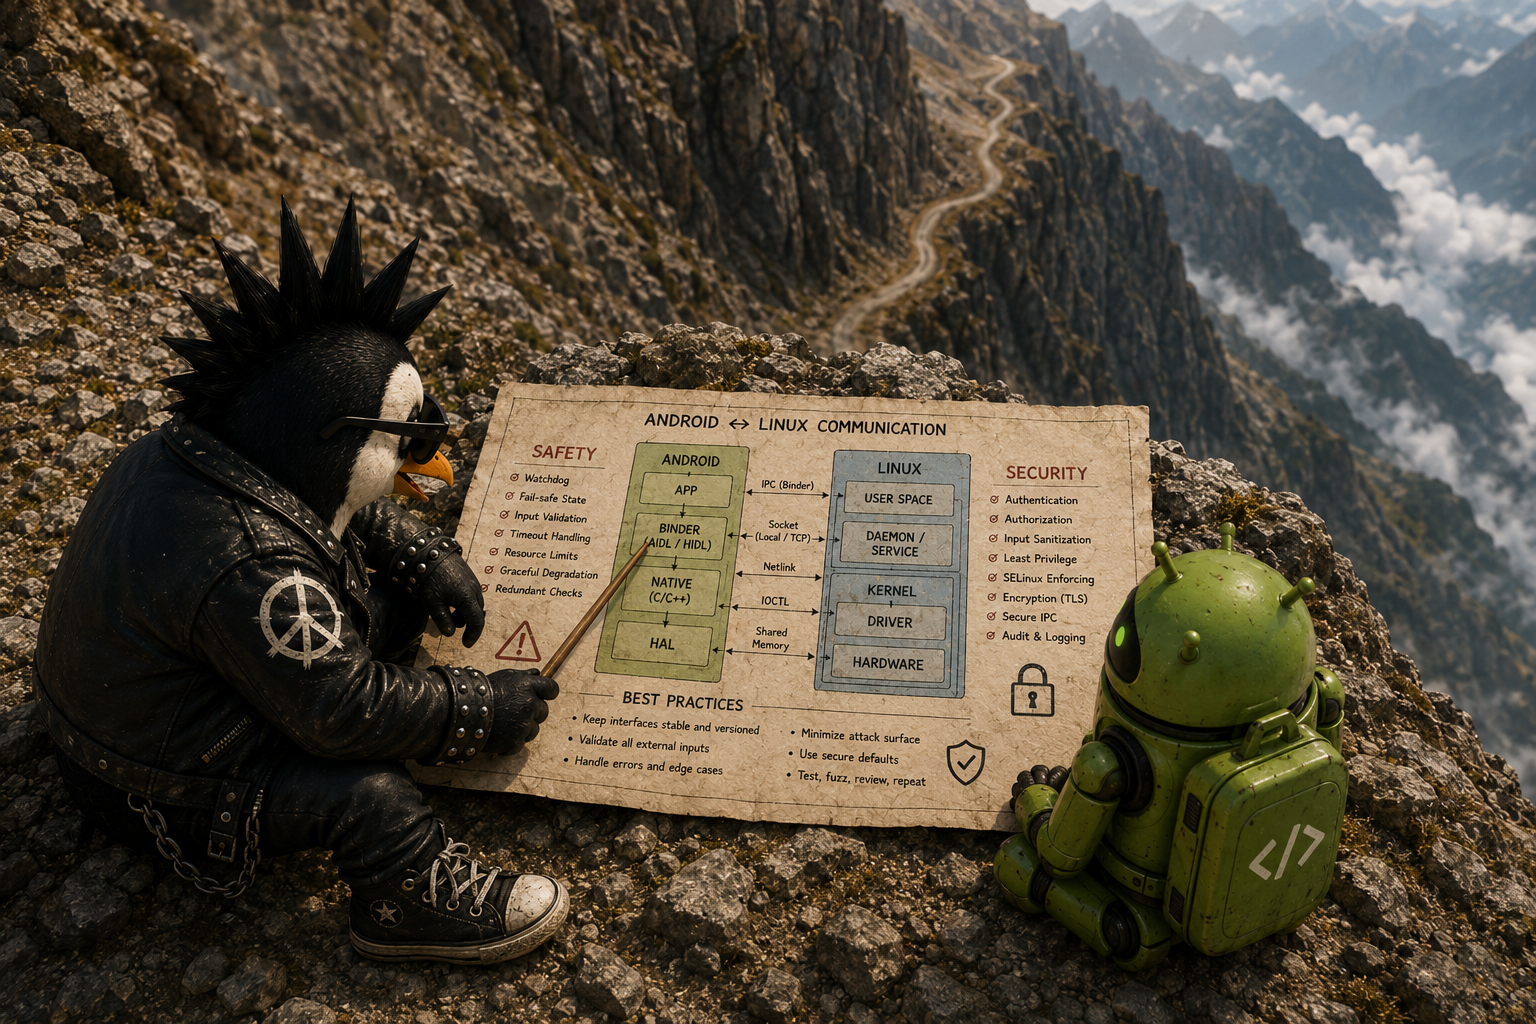
A while ago, I was sitting with a friend over coffee and we started talking about Android security. It was not supposed to be a design meeting. We…
Field notes, deep dives and build logs — newest first.
A while ago, I was sitting with a friend over coffee and we started talking about Android security. It was not supposed to be a design meeting. We…
Part 2: One Big Bucket: When Sharing a Secure World Becomes a Liability In Part 1, we walked through how TrustZone splits the processor into two hardware-enforced security…
A small note before we start. I originally planned to wrap this whole series up in two posts. But I read something on the internet recently — scientists…
strace is a diagnostic and debugging tool on Linux that allows you to trace the system calls made by a program during its execution. System calls are the…
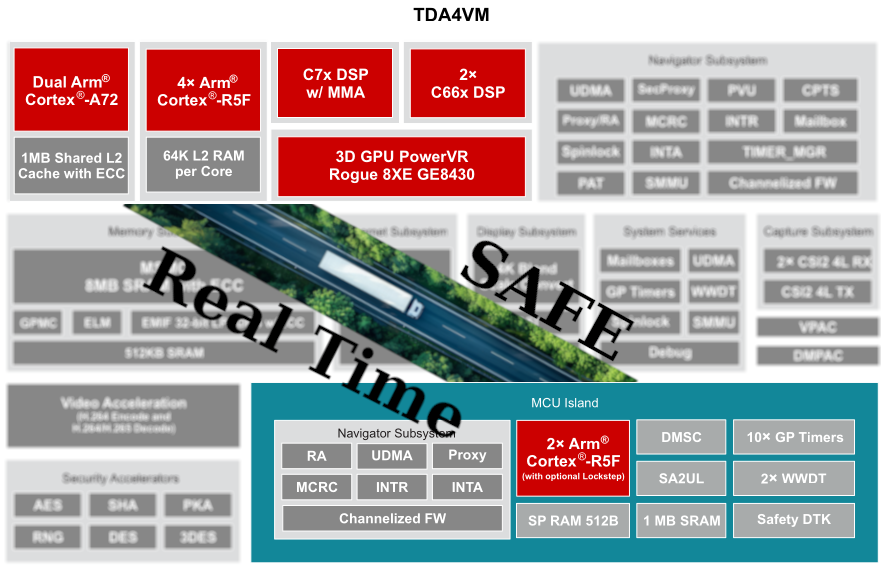
Before we get into the BeagleBone AI-64’s TDA4VM, let me start with something more personal. The first microprocessor I ever worked with was a Z80. It wasn’t soldered…
You know that feeling when you run into someone on the street and you’re almost convinced you’ve met them before? Or maybe they just remind you of someone…
In Part 1, I told a little bit of a story. We left the “stupid black boxes” era behind, looked at why embedded devices must have network-level protection,…
For a long time, embedded devices were just “stupid black boxes”, especially in domains like industrial control and automotive. To be fair, in their own time, these systems…
I’ve been using a BeagleBone AI-64 for my hobby projects for a while. I decided to stick with this board as long as I can—no extra budget for…